Crypto hackers exploit third-party Aave tool to steal 114 ETH
An external lending adapter designed for Aave was exploited, leading to the theft of 114 ETH valued at over $300,000, though the core Aave protocol remained completely untouched.

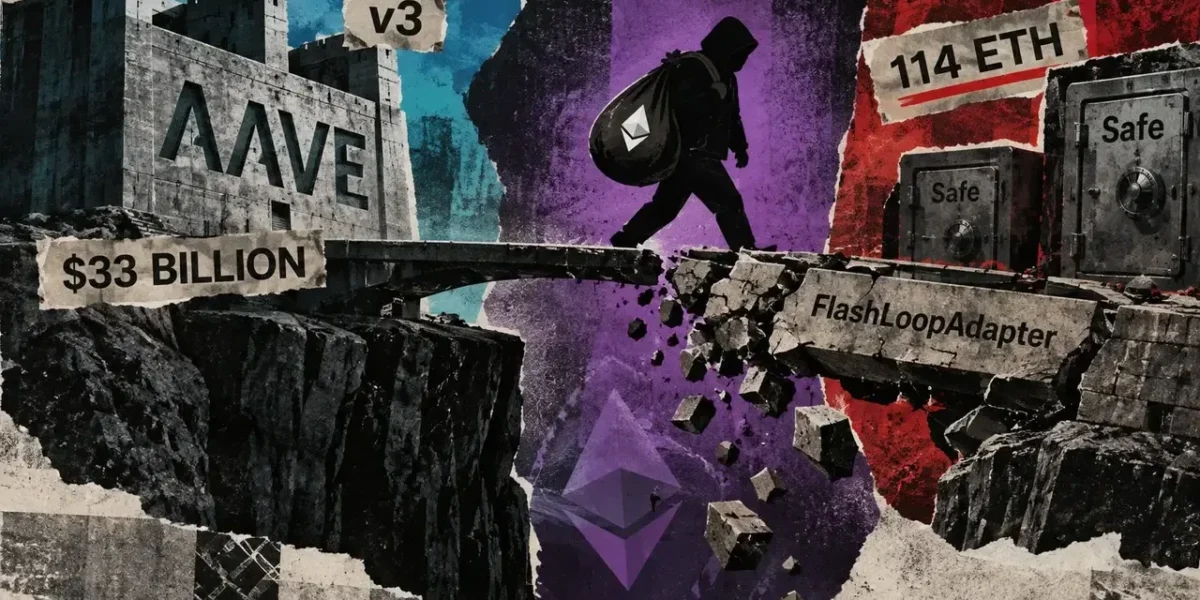
An external lending adapter designed for Aave fell victim to an exploit, resulting in the theft of approximately 114 ETH valued at over $300,000, though the core protocol itself was left untouched.
Blockchain security firm SlowMist reported on Oct. 2 that an attacker managed to breach two Safe multisig wallets by exploiting a vulnerability within the FlashLoopAdapter, which integrates with Aave v3 positions. The security flaw permitted the hacker to circumvent the adapter’s authentication verification, run arbitrary function calls, and empty collateral from the impacted wallets.
According to SlowMist’s calculations, direct losses reached approximately 114.09 ETH. The firm noted that the attacker additionally repaid around 1,300 WETH of debt during the incident in order to release collateral linked to the positions.
Stani Kulechov, founder of Aave, clarified that the security breach did not involve the core smart contracts of Aave v3. He stated:
“This is not Aave v3 contract, it’s third party external adapter built on top of Aave, zero effect on Aave v3.”
This separation is crucial for Aave, which stands as the premier decentralized lending protocol with a total value locked exceeding $33 billion. The security incident was confined to secondary infrastructure built on top of Aave.
Fake Safe bypass opened access to collateral
SlowMist pinpointed the vulnerability within the open() and close() functions of the FlashLoopAdapter, which typically verify whether the calling Safe has authorized the adapter to act as a module.
However, this verification process proved susceptible to spoofing.
SlowMist explained that the perpetrator deployed a counterfeit Safe contract programmed to invariably return a positive verification status whenever queried about module activation. Consequently, the adapter trusted the fraudulent authentication and advanced to its internal swap sequence.
A more critical weakness followed. The adapter granted callers the ability to define both the router and the calldata utilized in external contract interactions.
The attacker redirected the router toward the target Safe and provided parameters that triggered the Safe’s execTransactionFromModule function. Because the FlashLoopAdapter was genuinely authorized as a module on the targeted wallets, that command granted the hacker authorization to carry out transactions directly through the victims’ Safes.
SlowMist confirmed this method successfully extracted weETH along with collateral tied to Aave positions originating from two multisig wallets.
This event underscores a persistent vulnerability within decentralized finance, where a protocol’s native security can remain uncompromised while surrounding integrations introduce distinct vulnerabilities.
For Aave, immediate risk seems restricted to individuals utilizing the compromised adapter. Attention now turns to whether additional wallets activated this specific module, and if the developers of the adapter can discover other compromised positions before malicious actors exploit the identical authentication weakness again.
Frequently Asked Questions
01Was the core Aave protocol hacked?
No, Aave’s core smart contracts were not affected. The exploit occurred through a third-party external lending adapter built on top of Aave v3.
02How much money was stolen in the exploit?
The attacker stole approximately 114 ETH, valued at over $300,000, and repaid roughly 1,300 WETH of debt to unlock collateral.
03How did the attacker bypass authentication?
The attacker used a fake Safe contract that tricked the FlashLoopAdapter into believing the module was enabled, allowing them to execute arbitrary calls and drain collateral.