Wall Street ने NEAR में तब प्रवेश किया जब $4 बिलियन प्रति माह वाले एक ऐप को हैक कर लिया गया
NEAR के नए शुरू किए गए US एक्सचेंज-ट्रेडेड फंड को शुरुआती तनाव परीक्षण का सामना करना पड़ रहा है, क्योंकि $3.8 मिलियन के सुरक्षा शोषण ने टोकन को प्रभावित किया है और कीमत में 10% की गिरावट आई है।

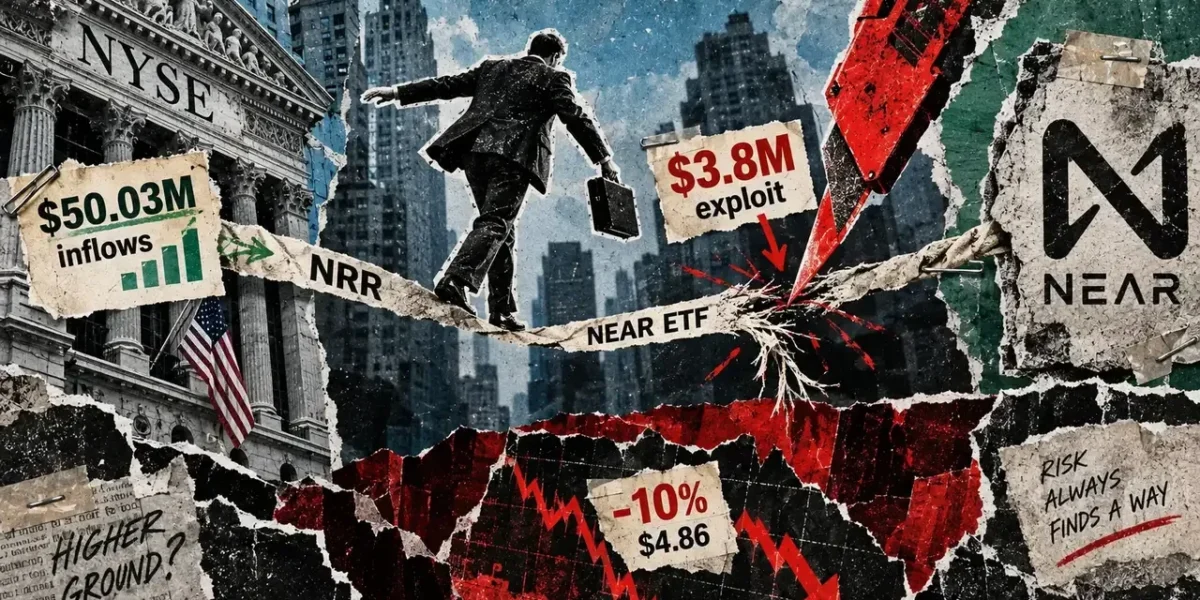
NEAR’s newly introduced US exchange-traded fund is undergoing its inaugural stress test just days after its debut, following a $3.8 million ecosystem security exploit that impacted the token.
The value of NEAR dropped roughly 10% to $4.86 after NEAR Intents reported a security breach involving its Omni deposit-and-withdrawal framework. This downward price movement occurred less than 48 hours after Bitwise made the token accessible to US ETF investors via its NEAR ETF, trading under the ticker symbol NRR.
The fund officially launched on NYSE Arca on Sept. 29, capturing $35.5 million in net inflows during its opening session. By Sept. 30, total net inflows climbed past $50 million, while aggregate net assets reached $52.8 million—representing approximately 0.76% of NEAR’s total market capitalization, based on figures from SoSoValue.
This timing subjects the fresh investment vehicle to an unusually early trial of investor confidence. While the ETF shields purchasers from the technical complexities of wallets, private keys, and native staking, its financial value remains tied directly to NEAR. Consequently, shareholders face exposure whenever external ecosystem troubles erode trust in the underlying token.
A $3.8 million exploit hits NEAR Intents
In a public statement shared on X, NEAR Intents announced a temporary suspension of its services following the detection of a bug that occurred during interactions between its Omni infrastructure and the Intents smart contract.
Initial losses were estimated at approximately $3.8 million, with project representatives committing to fully reimburse all impacted users. The development team successfully deployed a patch to resolve the contract vulnerability, allowing both NEAR Intents and near.com to resume operations following the brief shutdown.
Certain deposit and withdrawal pathways experienced extended downtime while engineers finalized upgrades to the Omni infrastructure across multiple supported networks, including BSC, Polygon, TON, Optimism, Avalanche, Stellar, and Scroll.
NEAR co-founder Illia Polosukhin clarified that the security breach was restricted to USDT transactions on BSC, noting that the SHIELD security framework utilized by NEAR Intents flagged abnormal behavior prior to halting operations. He confirmed that the team successfully isolated and fixed the issue within an hour.
The core NEAR blockchain maintained normal operations throughout the entire event. Representatives from NEAR Protocol emphasized that the exploit did not stem from any flaw within the main network or the native NEAR token, confirming that block generation and transaction processing proceeded without interruption.
This operational separation limits the direct impact on the Bitwise ETF, which provides exposure to NEAR itself rather than assets routed through NEAR Intents. Nevertheless, the swift market response highlights how rapidly application-level incidents can affect assets recently packaged for traditional financial markets.
The scale of the Intents business—which Polosukhin noted currently handles over $4 billion every month in trading and payment volumes—makes the security breach far more than a minor ecosystem issue, given its role as a primary bridge between NEAR and other external networks and applications.
Project organizers have formally notified law enforcement and are currently collaborating with blockchain analytics and security organizations to track the illicitly transferred funds. A comprehensive postmortem report is anticipated in the days ahead.
Polosukhin indicated that the broader ecosystem intends to broaden its deployment of formal verification tools and supplementary security measures moving forward, referencing ongoing efforts to establish a dedicated verification standard for NEAR smart contracts.
He stated:
“The crypto space is entering a new era of far more sophisticated cyber attacks. Recently, we have seen BitGet, Metamask, Lido all being targeted by criminals equipped with AI systems that are continuously trying to hack all infrastructure. As a space, we need to be far more vigilant and raise the bar on both onchain contract standards and offchain monitoring and proactive prevention.”
The ETF arrived after leverage had already started leaving
The recent downward price pressure also arrived within a market where speculative trading leverage had already receded significantly ahead of the NRR launch.
According to blockchain intelligence platform Santiment, open interest in NEAR-denominated futures reached a high of roughly 215 million NEAR on Sept. 21, eight days prior to the ETF rollout. By Sept. 29, that metric had decreased by about 21% to 169 million NEAR, even as the asset’s spot price climbed approximately 86% starting from Sept. 16.
Although dollar-denominated open interest kept rising for a few days to touch roughly $1 billion on Sept. 27, the shrinking quantity of NEAR tied up in derivatives signaled that speculative leverage was cooling down prior to the fund’s debut.
Santiment points out that this dynamic distinguishes the post-exploit price movement from a standard leveraged liquidation event. Spot market demand strengthened leading up to the launch while speculative exposure diminished, giving the incoming ETF inflows a more substantial function in shaping overall market structure.
While the initial two days of trading for NRR demonstrated clear institutional interest, the more severe test for the fund lies ahead in the wake of the security breach.
Should inflows persist despite the 10% price correction, it would indicate that institutional participants are comfortable separating localized application exploits from the broader investment thesis of the underlying blockchain network. Conversely, a reversal in fund flows would underscore how swiftly an ecosystem security incident can disrupt demand for an ETF that has traded for only a short duration.
अक्सर पूछे जाने वाले प्रश्न
01What caused the recent drop in NEAR’s price?
NEAR experienced a 10% price decline following a $3.8 million security exploit on NEAR Intents involving its Omni infrastructure, alongside broader market adjustments.
02Was the core NEAR blockchain compromised during the exploit?
No, NEAR Protocol confirmed that the base blockchain, network operations, and native NEAR token were unaffected, and block production continued without interruption.
03How does the Bitwise NEAR ETF (NRR) relate to the exploit?
The NRR ETF provides exposure to the underlying NEAR token rather than assets deposited within NEAR Intents, though market sentiment across the ecosystem can still influence the fund’s performance.