Nearly 5,000 BTC leaves Bitget as hackers begin laundering $387 million haul
Following a massive $387.5 million hack, nearly 5,000 Bitcoin left Bitget reserves as stolen funds were laundered through cross-chain bridges and mixing platforms, sparking a debate over THORChain intervention.

Following the reopening of withdrawals after a $387.5 million hack, nearly 5,000 Bitcoin has departed from Bitget’s tracked reserves.
Gracy Chen, Chief Executive Officer of Bitget, stated on Sept. 28 that the platform processed 9,585 withdrawal orders representing a total of 4,098.036 BTC as of 17:00 UTC+8, shortly after Bitcoin withdrawals were enabled again.
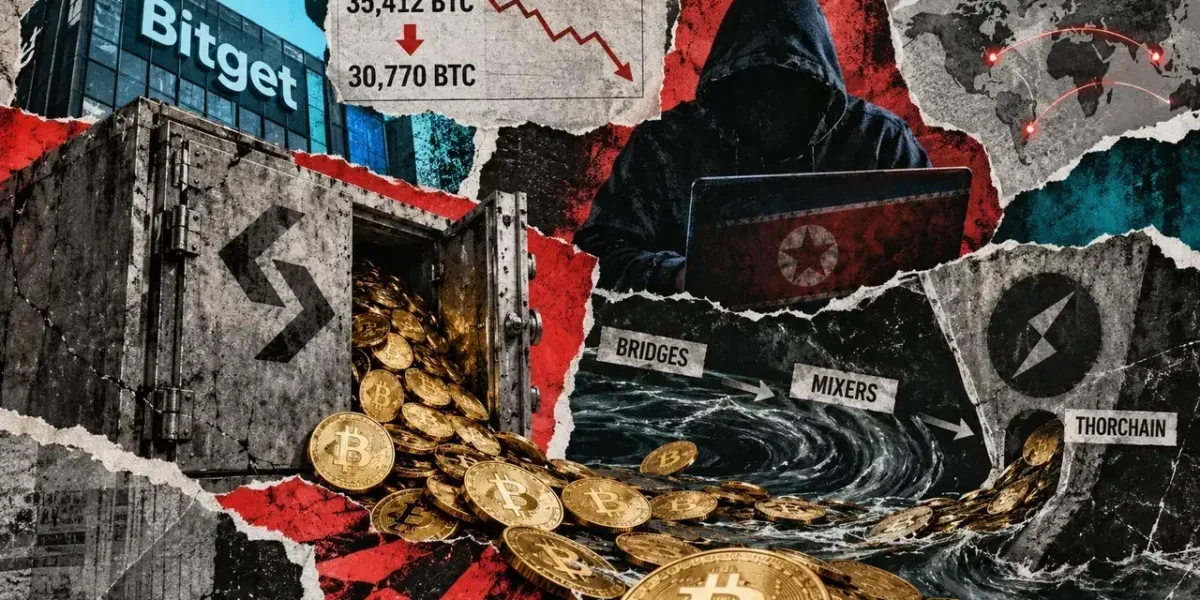
According to separate figures from DeFiLlama, Bitget’s tracked Bitcoin holdings dropped from 35,412 BTC down to approximately 30,770 BTC—a decrease of roughly 4,642 BTC. Based on current market rates, this reduction equals about $391 million worth of Bitcoin.
This decline in reserves exceeds the volume of customer withdrawal orders reported by Chen. Because DeFiLlama monitors exchange-associated wallet addresses, these fluctuations can also encompass internal wallet transfers or variations in address coverage rather than just user withdrawals.
Nonetheless, this swift outflow offers the initial gauge of user reaction after Bitget suspended withdrawals for a span of four days during its investigation into the largest security breach in its eight-year history.
Bitget brought back Bitcoin withdrawals at 08:00 UTC on Sept. 28 following extra verifications of its withdrawal systems. Ethereum withdrawals are planned for Sept. 29, USDT for Sept. 30, and the remaining tokens, fiat options, and peer-to-peer features are set for Oct. 2.
This service restoration coincides with Bitget’s efforts to convince clients that the breach left its private keys and cold-storage reserves untouched.
Chen noted that an internal investigation revealed attackers leveraged vulnerabilities within third-party tools to secure internal credentials. These credentials enabled the submission of fraudulent withdrawal commands that bypassed Bitget’s security checks.
The exchange has since isolated the impacted components, revoked and replaced internal login details, and overhauled access to vulnerable systems, according to Chen. Bitget also disabled the compromised third-party features while the supplier develops a patch.
Security firms such as Mandiant and SlowMist continue to provide forensic support and efforts to trace the missing funds. Bitget previously disclosed that the event targeted a critical backend part of its wallet architecture and that the vulnerability was fixed prior to reopening withdrawals.
Bitget has affirmed that users will not absorb any losses from the event and that its Protection Fund will absorb the deficit. Chen stated that the firm intends to use its own funds to bring the reserve back above $300 million within a week.
Stolen funds move as THORChain resists calls to intervene
At the same time, recovering the pilfered Bitget assets grows more complex as the funds fracture across cross-chain bridges, decentralized finance protocols, and privacy tools.
Blockchain analyst ZachXBT reported that Chinese criminal networks were laundering the exploit proceeds on behalf of hackers allegedly connected to North Korea. He indicated that the money was undergoing chain-hopping and being sent to mixing platforms like Wasabi.
ZachXBT also tied a member of this laundering ring to asset movements following the $292 million Kelp DAO exploit earlier in the year, noting similar patterns to those seen in attacks tied to the TraderTraitor campaign.
These laundering activities have placed THORChain at the center of an intensifying debate regarding whether permissionless networks ought to step in when stolen capital flows through their infrastructure.
THORChain maintains that it will not selectively freeze wallets or swaps, asserting that its function mirrors censorship-resistant networks like Bitcoin and Ethereum. Conversely, security firm GoPlus disputed this comparison, arguing that THORChain’s network design grants node operators capabilities that base-layer validators lack.
GoPlus highlighted THORChain’s threshold-signature vaults—where active nodes collectively sign off on outbound transfers—noting that releasing funds from these vaults demands active signing cooperation. The firm also pointed to per-chain signing freezes, network-wide pauses, and Mimir governance as proof that node operators can act collectively when desired.
This shifts the debate from whether THORChain possesses emergency tools to when its operators choose to deploy them.
GoPlus additionally referenced THORChain’s reaction to its own $10.7 million exploit in May, during which the network was paused as part of containment measures. The security firm contended that this exact emergency mechanism could be applied to addresses associated with the Bitget attackers.
THORChain rejected that argument, explaining that a network pause serves to safeguard the protocol itself and differs from intentionally censoring a specific user, wallet, or swap transaction. The protocol added that attacker addresses were not blacklisted during the May incident, insisting the network should stay neutral even when known stolen funds pass through it.
GoPlus accused THORChain of drawing financial advantage from that stance. The firm estimated that roughly 101.5 BTC, valued at approximately $8.5 million, had already left the protocol from the Bitget exploit, alongside another 27.63 million XRP, worth about $43 million, being swapped into Bitcoin.
Furthermore, the security firm mentioned THORChain’s involvement in laundering funds from the 2025 Bybit breach, where the attacker funneled hundreds of thousands of ETH via the protocol and yielded millions in fee revenue. GoPlus claimed this fee generation introduces a conflict of interest when node operators choose not to disrupt illicit transfers.
THORChain has rejected this framing, leaving the wider crypto space to grapple with whether decentralized protocols equipped with emergency override controls ought to remain transaction-neutral when utilized to launder proceeds from major exploits.
For Bitget, this ongoing debate carries immediate practical implications. As Ethereum, USDT, and other withdrawal channels reopen, investigators are racing to reclaim funds that are already being broken down across multiple chains and channeled through networks whose operators may decline to intervene.
Frequently Asked Questions
01How much was stolen in the Bitget security incident?
The security incident involved a haul valued at $387.5 million.
02Are customer funds safe after the Bitget hack?
Bitget has stated that customers will experience no losses from the breach, and its Protection Fund will cover the shortfall.
03Why are stolen funds moving through THORChain?
Hackers are laundering the stolen assets across various bridges and cross-chain protocols, including THORChain, which maintains a stance of transaction neutrality and refuses to selectively block wallets.