Bitget had 30 minutes to contain its hack before $290 million started moving
Crypto exchange Bitget had a critical 30-minute window to contain a major security breach before malicious actors drained hundreds of millions of dollars from its wallets, according to a timeline from blockchain security firm Hypernative.

Crypto exchange Bitget identified unauthorized wallet transactions approximately 30 minutes before malicious actors began sweeping away hundreds of millions of dollars, intensifying scrutiny over why its incident response failed to stop the breach.
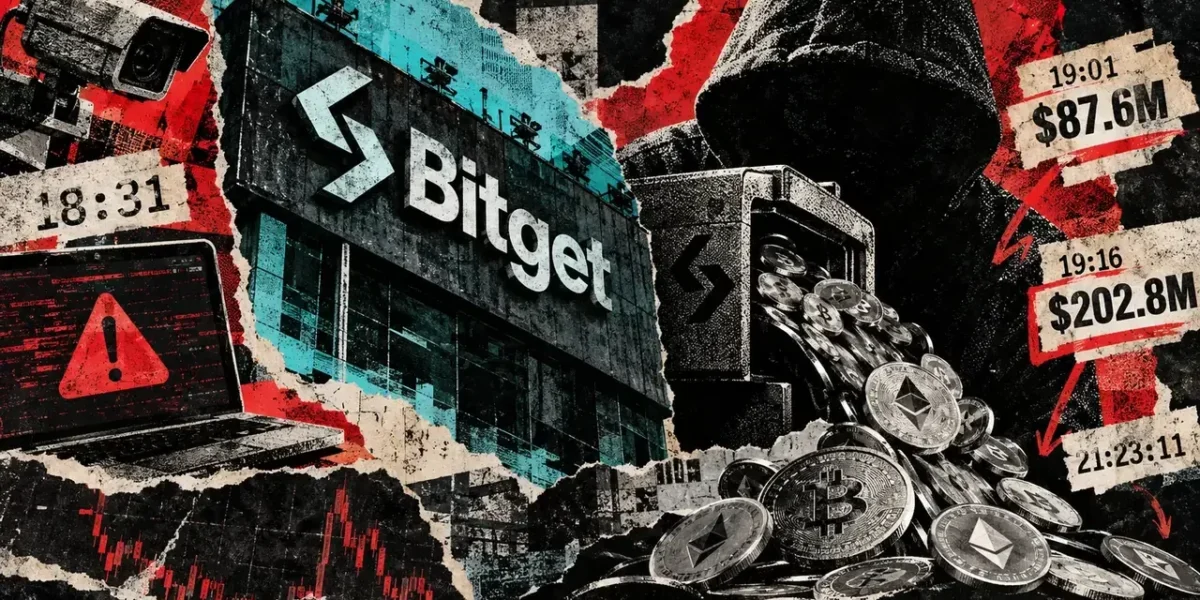
According to the exchange, its monitoring systems flagged the suspicious transactions at 18:31 UTC on September 24, prompting the security team to immediately initiate emergency protocols.
Yet, findings from blockchain security firm Hypernative reveal that the vast majority of funds vanished afterward: $87.6 million drained from hot wallets at 19:01, followed by another $202.8 million pulled from warm wallets at 19:16.
Together, these two rapid-fire events—each executed in a mere 24 seconds—made up roughly three-quarters of the $387.5 million that Bitget confirmed was funneled to addresses controlled by the attacker.
This timeline indicates that Bitget had roughly a 30-minute window following its initial warning to block the first significant wave, and about 45 minutes before the largest transfer peak. Consequently, attention has shifted away from how the hacker initially breached the system and toward how the exchange reacted after its own monitors raised red flags.
Hypernative noted that the hacker first tested the vulnerable path at 18:31 by moving 0.84 ETH and 93 TRX to fresh addresses. Following a roughly 28-minute pause, the perpetrator transferred $34.75 million in USDT at 18:58 before ramping up the multi-chain drain.
Bitget’s containment controls failed to stop the signing?
Bitget reported that its internal inquiry showed the attacker breached a backend component within its wallet architecture, manipulated withdrawal information, and deceived the authorization mechanism into greenlighting the transactions. The firm emphasized that private keys remained uncompromised.
This specific exploit vector makes the response timeline especially critical. Hypernative pointed out that the transactions were executed using Bitget’s own wallets, bearing enough resemblance to routine user withdrawals to slip past infrastructure checks.
The security specialists outlined several safeguards that could have halted the incident following the initial alert.
One such measure would mandate that every signed transfer match an independently recorded customer withdrawal or validated treasury transaction. Implementing this check would have blocked a compromised backend service from generating independent authorizations.
Furthermore, Hypernative spotted atypical transaction details in the hacker’s payloads, such as gas limits that strayed from Bitget’s standard withdrawal procedures. Screening proposed transactions against baseline parameters typically issued by the exchange could have flagged the 18:31 test transaction well before the massive outflows commenced.
Velocity thresholds offered another safeguard. Hypernative observed that warm wallets distributed $202.8 million across five different networks in just nine seconds at 19:16. Enforcing caps on transfer volumes within tight timeframes for distinct wallet tiers, alongside mandatory secondary approvals, could have delayed or prevented the bulk of that outflow.
Most importantly, Hypernative argued that anomaly alerts should prompt an automated freeze of the compromised signer rather than depending on manual human action. Instead, transfers tied to the attacker persisted until 21:23 UTC—nearly three hours after Bitget stated it first detected the issue.
Bitget stated that it has since patched the flaw and verified that no additional unauthorized transfers occurred after the situation was contained. Forensic investigations continue with the assistance of Mandiant and SlowMist.
The lingering question centers on how Bitget’s security architecture handled the 18:31 notification, and why the vulnerable signing path stayed active long enough for approximately $290 million to leave during the subsequent two major waves.
Frequently Asked Questions
01When did Bitget detect the unauthorized wallet transfers?
Bitget’s systems flagged the unauthorized transfers at 18:31 UTC on Sept. 24.
02How much money was ultimately moved to attacker-controlled addresses?
Bitget stated that a total of $387.5 million was moved to attacker-controlled addresses.
03Were Bitget’s private keys compromised in the attack?
According to Bitget’s investigation, private keys were not compromised; instead, the attacker breached a backend system in the wallet infrastructure and spoofed withdrawal data.
04Which firms are involved in the forensic investigation?
Mandiant and SlowMist are involved in the ongoing forensic investigation.