Lazarus Group का पर्दाफाश करने के लिए ZachXBT ने $1B के क्रिप्टो सिंडिकेट में घुसपैठ की
Blockchain sleuth ZachXBT infiltrated a Chinese money laundering network by posing as a regular cryptocurrency customer, trading stablecoins to expose a syndicate laundering funds connected to the Lazarus Group and the Bybit hack.

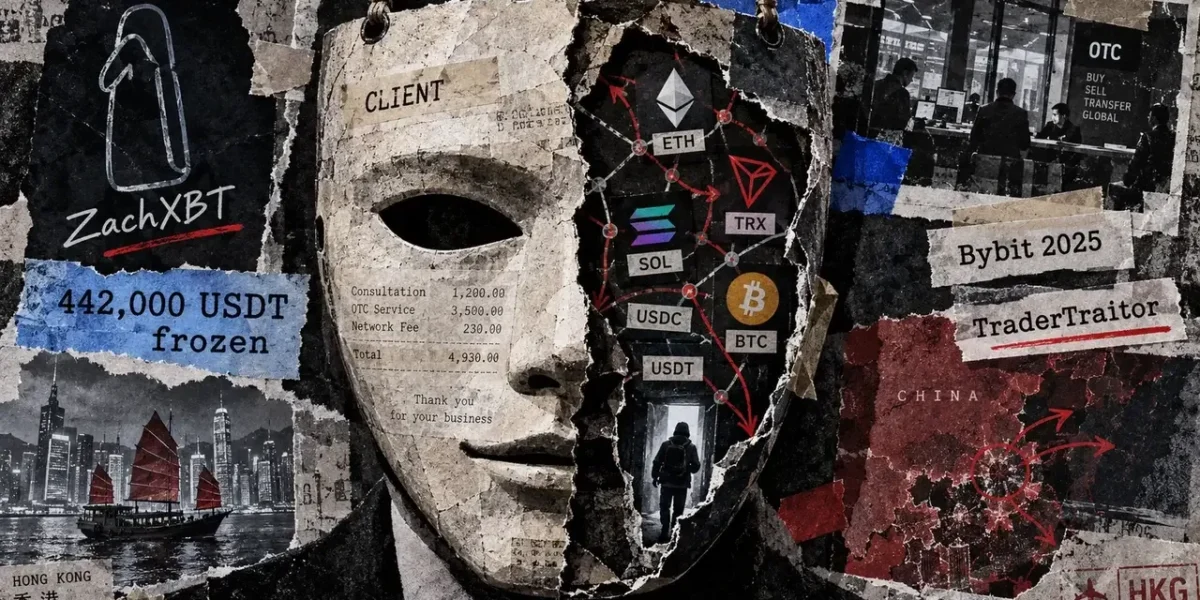
Blockchain sleuth ZachXBT revealed that he successfully infiltrated a Chinese money laundering network by posing as a regular cryptocurrency customer and executing a series of stablecoin trades.
In a disclosure published on Oct. 5, he claims the illicit ring laundered upward of $1 billion connected to exploits carried out by the Lazarus Group.
To establish credibility with a network operative going by the Telegram alias Jimmy Green, ZachXBT stated he fronted 349,700 USDC. According to his findings, these frequent trades opened the door to private discussions regarding the transfer of assets stolen during the 2025 Bybit hack.
He noted that his tracking uncovered a group of addresses tied to more than $12 million in Bybit funds, alongside a subsequent freeze of 442,000 USDT executed by Tether.
Becoming a client
The investigation kicked off following the February 2025 Bybit breach, when ZachXBT spotted at least 15 public Telegram and Discord accounts seeking assistance with orders that he later tied to the stolen capital.
He reached out to several of those accounts, including Jimmy Green, the handle used by the person with whom he eventually traded assets.
On March 6, 2025, ZachXBT funded a fresh Ethereum wallet with 349,700 USDC to prepare for transactions with his contact. The scheme involved trading his Ethereum-based USDC for the contact’s Tron-based USDT, followed by extra transactions aimed at cementing trust.
As rapport grew through these successive trades, ZachXBT noted that the operative began sharing advance details about upcoming movements of North Korean-linked Bybit funds, alongside operational insights regarding activities in mainland China and Hong Kong.
As one instance, he recalled the contact predicting that funds would shift to Solana the following day—a prediction that materialized right on schedule.
On March 12, 2025, the contact shared a screenshot of a cross-chain transfer. ZachXBT verified the transfer by matching its figures and timestamp with a transaction recorded on the THORChain explorer just minutes after the message arrived.
The operative also provided three Solana wallet addresses, which ZachXBT said revealed a cluster of over $12 million in Bybit exploit capital moving across Bitcoin, Ethereum, Tron, and Solana.
Separately, he pointed out that Tether ultimately froze 442,000 USDT associated with this cluster. While that figure marks the specific frozen amount noted in this phase of his inquiry, the broader cluster figure reflects the total volume of funds he claims to have tracked.
The findings extend beyond the Bybit incident. ZachXBT pointed out that the contact referenced a group whose funds were frozen back in 2024, which aligned with an on-chain freeze of 332,000 USDC connected to the Poloniex exploit.
The Bybit backdrop and the cost of access
In an alert issued on Feb. 26, 2025, the FBI reported that North Korea had pilfered roughly $1.5 billion in digital assets from Bybit on or around Feb. 21, attributing the malicious campaign to a cluster known as TraderTraitor.
At that time, federal authorities noted that a portion of the stolen cryptocurrency had been converted into Bitcoin and dispersed across thousands of wallets spanning multiple blockchains, urging private-sector firms to block transactions linked to those laundering endpoints.
The syndicate’s aggregate volume and its connection to Jimmy Green are solely ZachXBT’s conclusions and are distinct from the FBI’s official attribution of the theft.
Accusations pointing to a Chinese over-the-counter broker first emerged in October 2024. This latest report details how ZachXBT gathered intelligence by stepping directly into the role of a trading participant.
ZachXBT noted that he fronted 349,700 USDC for the operation and incurred a 5% loss on every order. The capital advanced is separate from his overall net loss, a figure he left unquantified in his public statements.
He concluded with a call for ongoing individual donations and foundation grants to back high-stakes investigations, emphasizing that the intelligence gathered from these trades successfully aided in freezing assets connected to the Bybit breach.
अक्सर पूछे जाने वाले प्रश्न
01Who is ZachXBT?
ZachXBT is a well-known independent blockchain investigator who uses on-chain data analysis to expose cryptocurrency scams, hacks, and money laundering syndicates.
02What was the Bybit exploit?
The FBI reported that North Korea stole approximately $1.5 billion in virtual assets from Bybit on or around February 21, 2025, utilizing methods attributed to the TraderTraitor campaign.
03How did ZachXBT infiltrate the syndicate?
He posed as a regular cryptocurrency client, funding 349,700 USDC to execute repeated stablecoin trades and build trust with a contact using the Telegram alias Jimmy Green.