Locked liquidity did not stop this $14 million crypto pool drain
A Bitquery investigation reveals that the 79thVault token pool on PancakeSwap suffered a $14.35 million USDT drain after internal token permissions bypassed locked liquidity receipts.

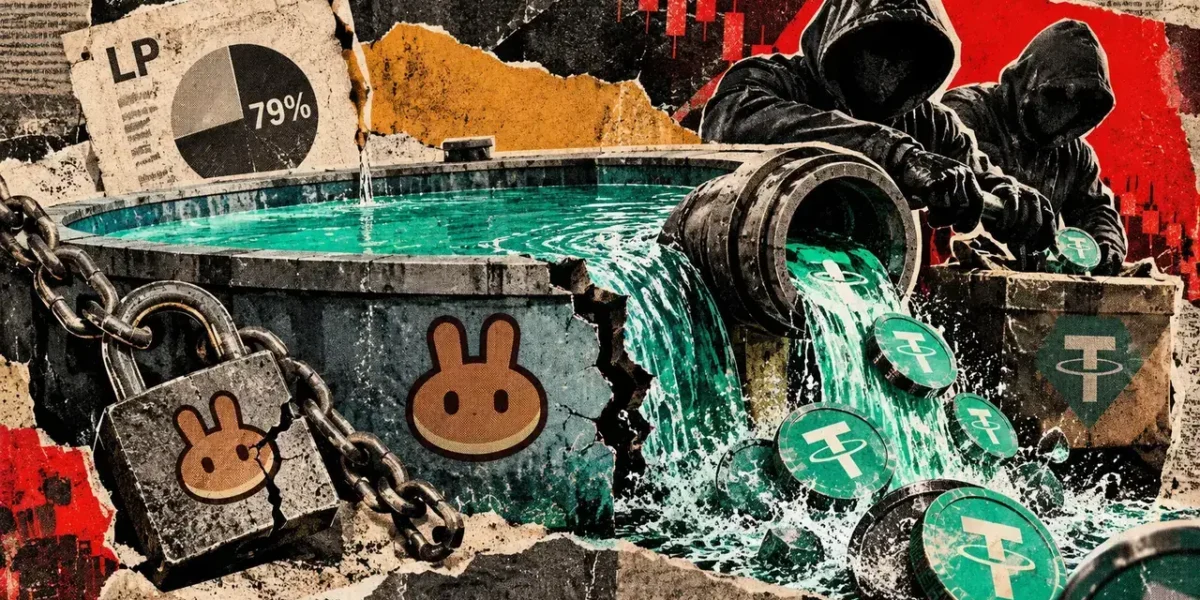
According to a Bitquery investigation published on Oct. 8, the PancakeSwap pool for 79thVault’s token, 79AU, suffered a loss of $14.35 million in USDT on Oct. 7 executed via two selling wallets.
Bitquery discovered that although 79% of the pool’s liquidity-provider receipts were burned, an internal permission within 79AU allowed tokens to exit the pool without any payment. These tokens were subsequently sold for USDT, entirely circumventing the requirement to redeem a liquidity receipt.
Liquidity-provider (LP) tokens are defined in PancakeSwap’s V2 documentation as receipts that signify a provider’s portion of a pool, distinct from the pair of assets being traded by users.
Standard redemption is outlined in the exchange’s liquidity guide: a provider chooses a specific share to withdraw and gets back both paired tokens. Sending these receipts to a dead or inaccessible address blocks their redemption, yet it does not stop swaps, because trading involves exchanging the underlying assets directly rather than cashing out a liquidity position.
Within PancakeSwap’s archived pair contract, distinct functions manage LP redemption, swaps, and the synchronization of recorded reserves with actual token balances. While the swap function verifies input tokens without requiring the surrender of LP receipts, the reserve-update function reads balances straight from the underlying token contracts. Consequently, burning LP receipts fails to alter those contracts’ balance rules or strip a privileged address of its token permissions.
What remained exposed
Bitquery pinpointed two pull-authorized addresses at 12:53 UTC on Oct. 8: the deployer wallet along with a newly authorized wallet. Read-only simulations performed using either address indicated that approximately 95% of the pool’s remaining 79AU could be removed, though these simulations did not transfer any actual funds.
At the time of the same snapshot, a single wallet held the unburned 21% portion of LP receipts, retaining standard redemption rights for that specific share.
Verifying whether the reported exposure affecting 79AU has truly concluded necessitates a new inspection of that transfer permission.
Frequently Asked Questions
01How did the 79AU pool drain happen if liquidity was locked?
While 79% of the pool’s liquidity receipts were burned (locked), a permission inside the 79AU token contract allowed tokens to leave the pool without payment. These tokens were sold directly for USDT without needing to redeem a liquidity receipt.
02Did burning LP receipts fail to protect the pool?
Yes. Burning LP receipts prevents standard redemption, but it does not alter the underlying token contracts’ balance rules or revoke privileged transfer permissions that bypass normal swapping mechanisms.
03What is the status of the remaining funds?
Read-only simulations indicated that roughly 95% of the remaining 79AU in the pool could be removed by authorized addresses, while one wallet held the unburned 21% of LP receipts with standard redemption rights.